Asset inventory for OT
In 14 pages, the whitepaper shows how to build an asset inventory, keep it current, and use it for maintenance and security.
Who is the whitepaper for?
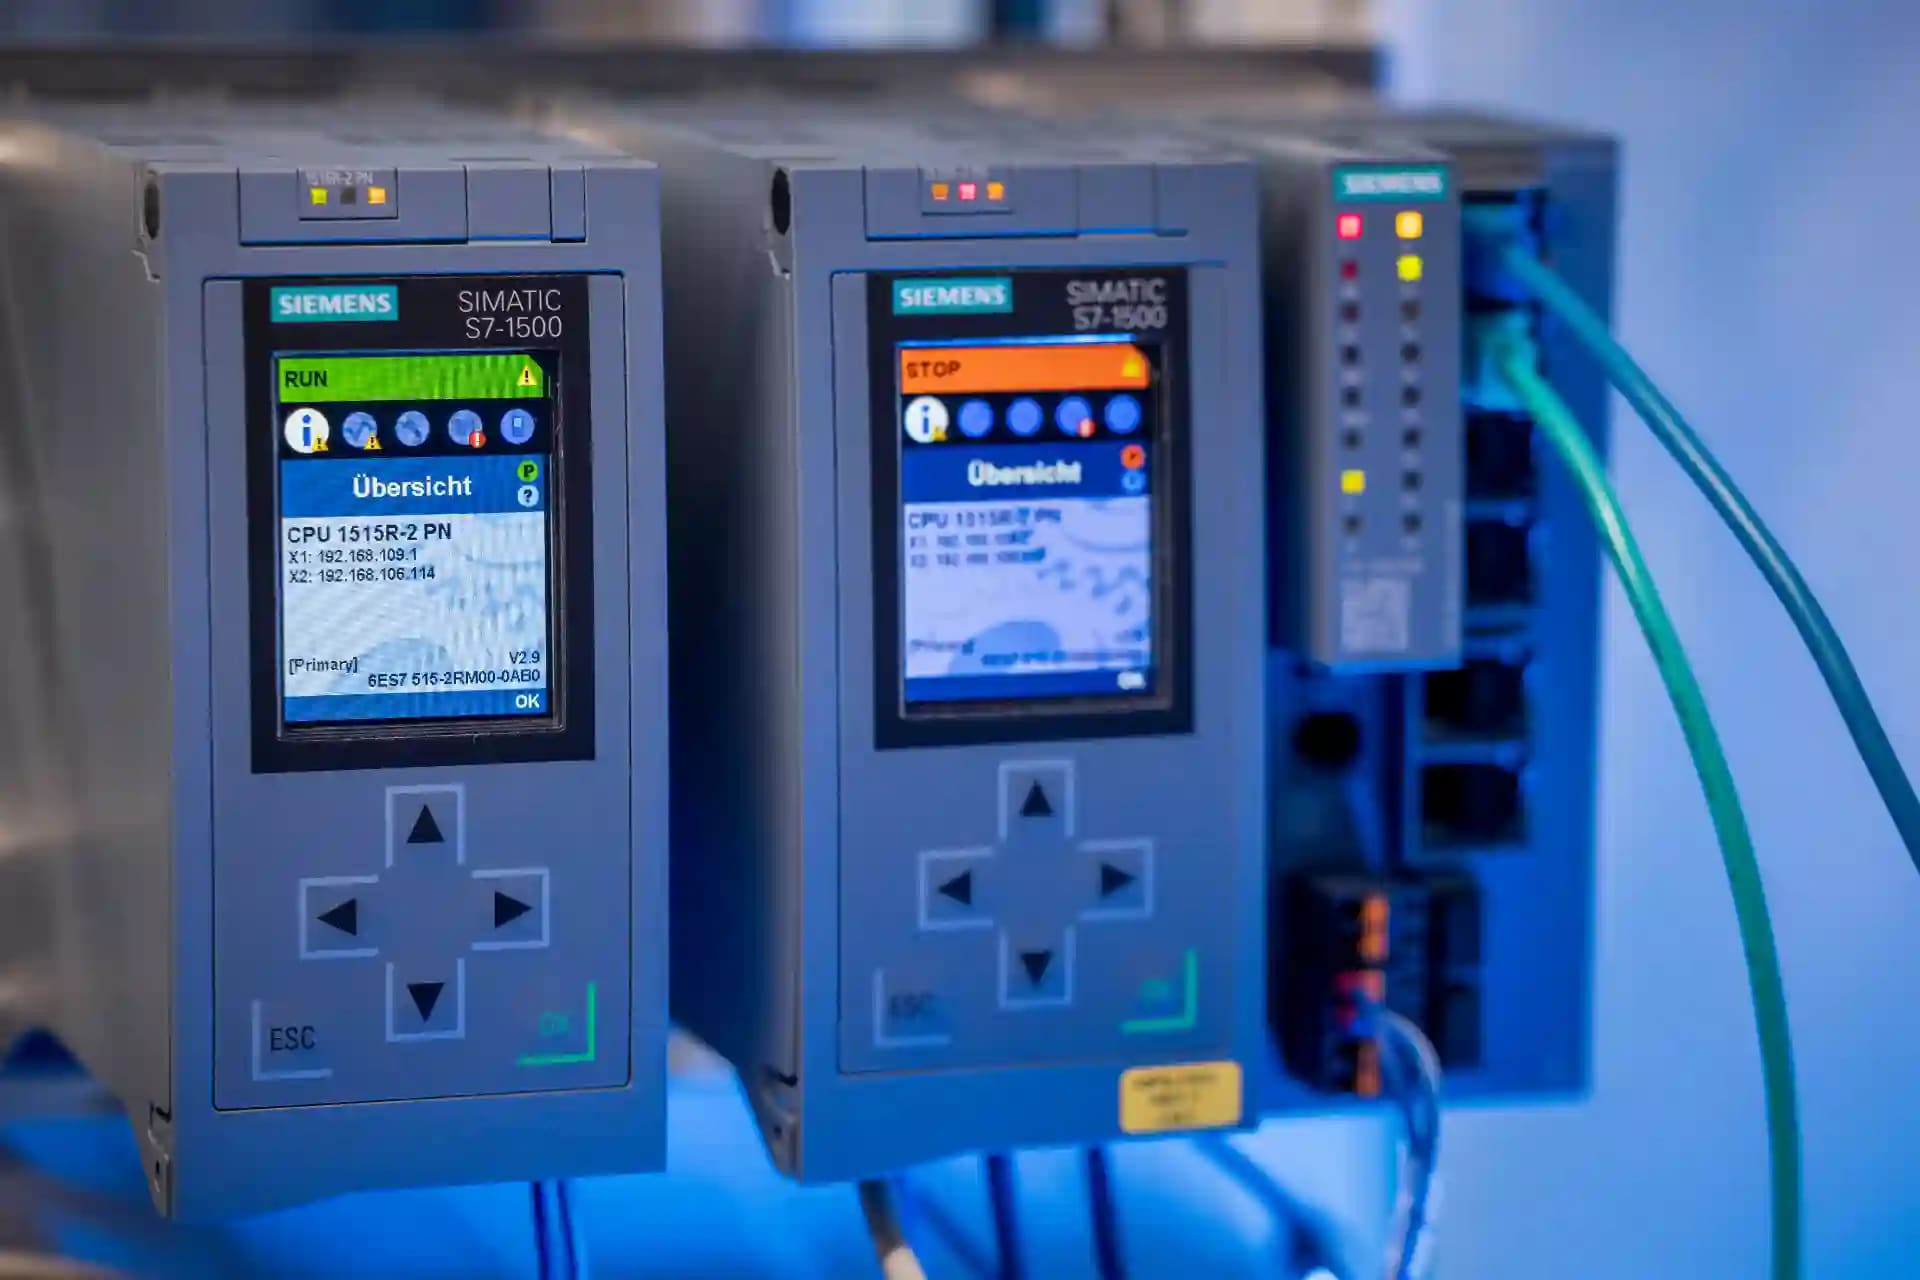
When a line stops or a security advisory arrives, your team needs quick answers: what is installed, what is affected, and who can act? The whitepaper is written for machine builders, operators of automated plants, and maintenance teams. It focuses on controllers (PLCs), HMIsAn HMI is an operator interface through which people observe and control machines, plants, or processes., drives, engineering PCs, servers, and network components.
What's inside
- Which data you need: a core record of identifier, technical state, installation location, communication, ownership, and impact on production.
- Collecting the installed base: documentation, passive observation of network traffic, approved device queries, and on-site checks complement each other, as NIST SP 800-82NIST guide to operational technology and industrial control system security. also describes.
- Handover and upkeep: who updates what in the inventory at commissioning, device replacement, and decommissioning.
- Preparing security measures: planning network segments, access, vulnerabilitiesA vulnerability is an exploitable weakness in software, hardware, configuration, process, or architecture., and recovery with data from the inventory.
- A maintenance example: a vendor advisory affects a packaging line, step by step to a confirmed new state.
- Starting with one plant: four steps for a pilot area, from an operational question to routine upkeep.
Why it matters now
The NIS2 directiveConsolidated text of EU Directive 2022/2555 (NIS2) on measures for a high common level of cybersecurity across the Union. requires affected entities to manage risk and handle vulnerabilitiesA vulnerability is an exploitable weakness in software, hardware, configuration, process, or architecture.. The Cyber Resilience ActOfficial EUR-Lex text of Regulation (EU) 2024/2847 covering manufacturer obligations, essential cybersecurity requirements, technical documentation, conformity assessment, SBOMs, and CE marking. applies to manufacturers of products with digital elements; its main obligations apply from 11 December 2027. The EU Machinery RegulationOfficial EUR-Lex text of the EU Machinery Regulation covering conformity, CE marking, protection of compliance-relevant software and data, and the safety of control systems. applies from 20 January 2027 and requires, among other things, that safety-relevant software is identifiable and protected against corruption.
A maintained inventory provides the data for these tasks. It does not replace risk assessmentA risk assessment evaluates threats, impacts, and protection needs so security measures are set based on risk rather than uniformly. or conformity assessment. The CISA guidanceJoint agency guidance published in August 2025 on building an OT asset inventory with taxonomy, data management, and lifecycle maintenance. describes the inventory as the foundation for further protective measures.
Download the whitepaper
The whitepaper is 14 pages long, written in British English, and free of charge. Enter your email address and we will send you the link to the PDF. Would you rather talk about a specific plant? Contact us.
Download the whitepaper
Get the PDF delivered to your inbox.
Related products and solutions
secnostic inventory
Devices, software, and ownership in one place. See what is there and how it is connected.
secnostic sensor
Discovers devices and connections in the network. Add the actual findings to your existing records.
Machine builders
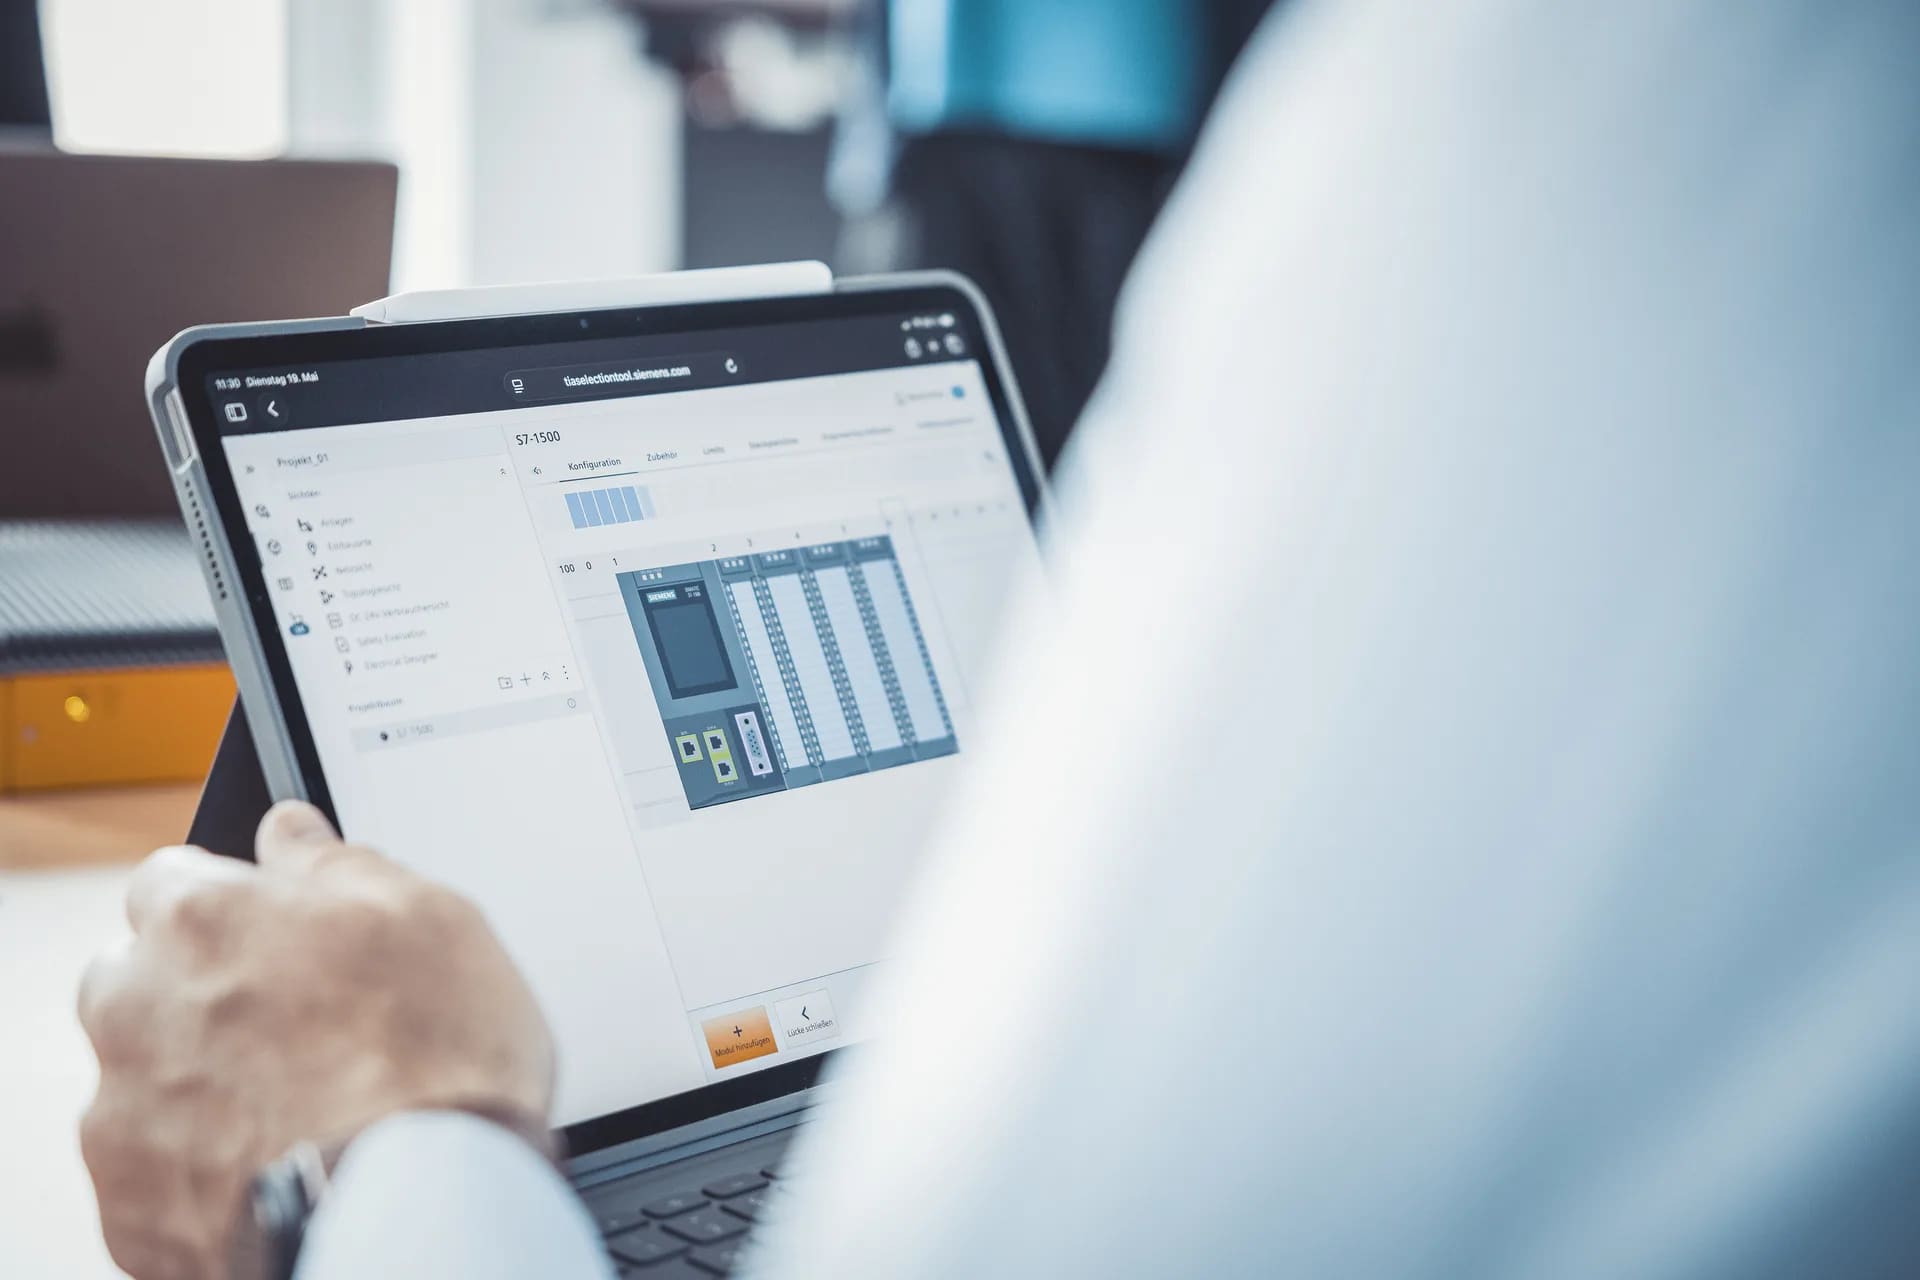
Document components and software versions in delivered machines. Find changes and affected machines when providing service.
Production
Discover machines and connections in a production line. Identify dependencies during maintenance and outages.